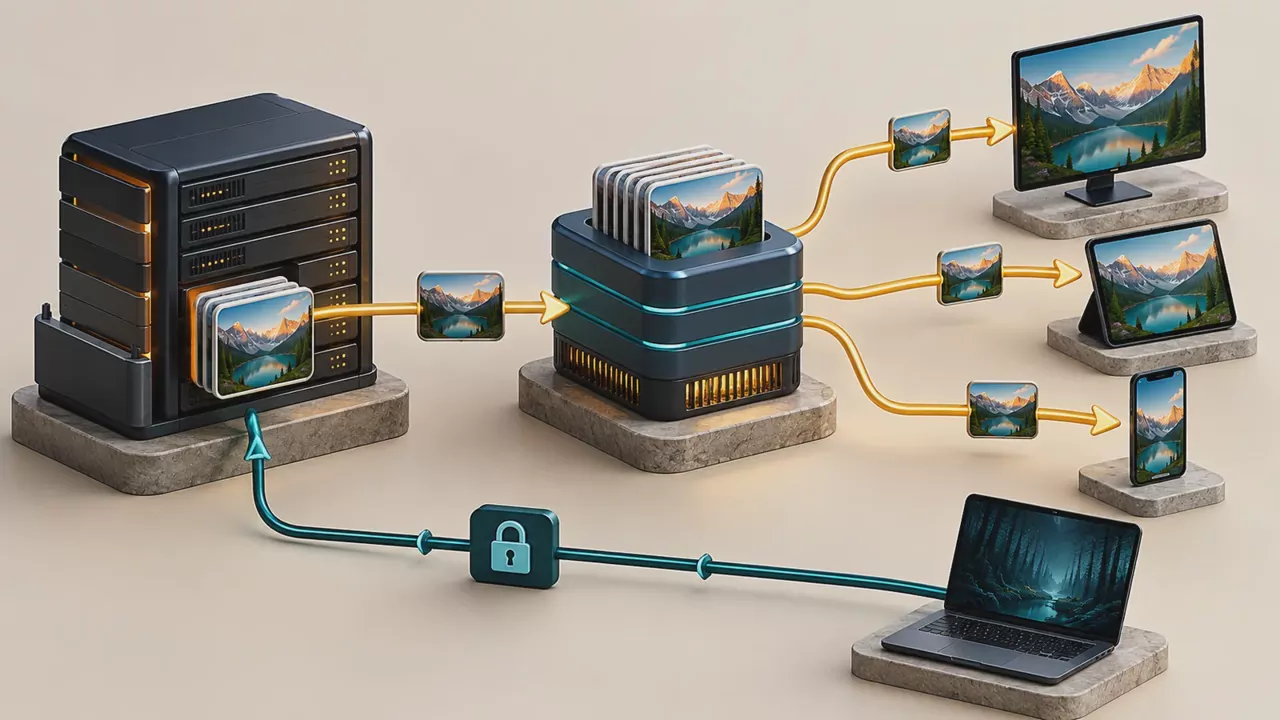
When a CDN helps—and what a quick test cannot tell you
Turning a CDN off and on taught us more about measurement and cache configuration than a simple faster-or-slower verdict.
 Zukatek Journal5 min read
The project draft describes turning a CDN off, then enabling it again a few days later. The useful lesson is not that either configuration always wins. It is how easily an incomplete test can support an overly confident conclusion.
Why the proxy was disabled
The page felt slow. An early test recorded 348–838 ms through the CDN against an internal response around 3 ms. But the test ran from the origin server, out through the CDN and back to itself. That is not the route a user takes.
A later test from a machine in Vietnam recorded:
Route | TLS timing | TTFB | Total |
|---|---|---|---|
CDN proxy | 0.13–0.16 s | 0.31–0.49 s | 0.32–0.50 s |
Direct | 0.06–0.08 s | 0.08–0.10 s | 0.10–0.13 s |
This is not a complete controlled comparison. The routes tested different applications on the same server. TTFB includes their different processing work.
The TLS column is not conclusive either. We need to know whether it represents the TLS phase alone or a cumulative curl timestamp, whether connections were reused, and which protocols were negotiated. The table does not establish a fixed 70–80 ms CDN penalty.
An unfavorable route to the edge is one possible explanation, but identifying that requires routing evidence and the edge location code. Latency alone does not establish the location.
The team disabled the proxy at the time. These figures alone do not prove that was the better performance choice.
Why it was enabled again
The draft later records these ranges for the same page:
Site | Before, direct | After, CDN with caching |
|---|---|---|
| 0.10–0.13 s | 0.11–0.13 s |
The ranges overlap in the samples recorded. An accompanying header was:
cf-cache-status: REVALIDATEDThis means the cached resource was validated with the origin before being served. It does not prove there was no origin request or that the edge was in Vietnam. Headers, logs and controlled repeats are needed to explain the result.
A CDN may also provide DDoS mitigation and reduce direct origin exposure when DNS and firewall rules are configured correctly. It does not guarantee the origin IP has never been exposed.
The project account also describes the CDN accepting port 80 traffic while some direct international connections could not reach the origin. That is a separate operational observation, not proof of a universal CDN advantage.
Ask what can be cached
Content | Potential benefit | Important condition |
|---|---|---|
Images, CSS, JavaScript | Often substantial | Long caching needs versioned or hashed URLs and no private content |
Public pages that change infrequently | Often useful | Choose freshness and invalidation rules deliberately |
Authenticated pages | Depends | Usually bypass shared caching; routing and protection may still help |
Write APIs | Depends | Do not cache responses casually; protection may still be useful |
Origin distance and cache hit rate matter. For dynamic content, include routing, connection management and protection in the evaluation rather than assuming the proxy is only an added cost.
Three operational costs to plan for
1. Client IP handling changes
The origin sees connections from the proxy. A rate limiter can accidentally treat unrelated visitors as one client if it keys only on that address.
Trust forwarded client-IP headers only from authenticated, trusted proxies. Restrict origin traffic appropriately and configure the proxy chain. Accepting an IP header from arbitrary clients permits spoofing.
The draft also describes shared logs for a proxied and an unproxied application. An automatic ban based on those logs could block a CDN address range. Separate the logs and review the ban rules before enabling enforcement.
2. An old control file can delay an update
The draft reports an outdated service worker with a cache age of 6,411 seconds. The old worker silently discarded newly introduced notification kinds.
For stable worker URLs and runtime configuration, use an appropriate revalidation policy such as Cache-Control: no-cache. Check CDN overrides and the worker's installation and activation lifecycle too. no-cache permits storage but requires validation before reuse; no-store prohibits storage. Hashed application assets can still use long caching.
3. Origin certificates have a specific trust scope
Some CDNs supply origin certificates trusted by that CDN rather than ordinary browsers. Disabling the proxy can then expose a certificate browsers reject.
The project used a publicly trusted Let's Encrypt certificate at the origin to support both configurations. Check the trust scope of your own certificate before changing the route.
How to decide
Test the same content from real user locations, direct and proxied.
Record cache state, protocol and connection reuse.
Estimate how much traffic can safely use shared caching.
Include protection and operational requirements in the decision.
Repeat after deployment rather than relying on a provider's promise.
Figures are retained from the October 2026 Zukatek draft and were not independently verified. The first table compares different applications and must not be used as a CDN benchmark.
References: Cloudflare cache responses, MDN Cache-Control.
You might also like
Seven traps when backing up and moving a database
A backup that restores on a development machine may still fail at the destination. Check versions, secrets, constraints, files and cleanup scope.
Read the article
Server optimization: measure first, change second
An internal response around 3 ms does not explain a user's full wait. Separate processing, network time and asset loading before upgrading a server.
Read the article
Three problems small teams face—and how to tackle them before buying software
Scattered knowledge, repetitive work and missed customer inquiries often need a clearer process before they need another subscription.
Read the article